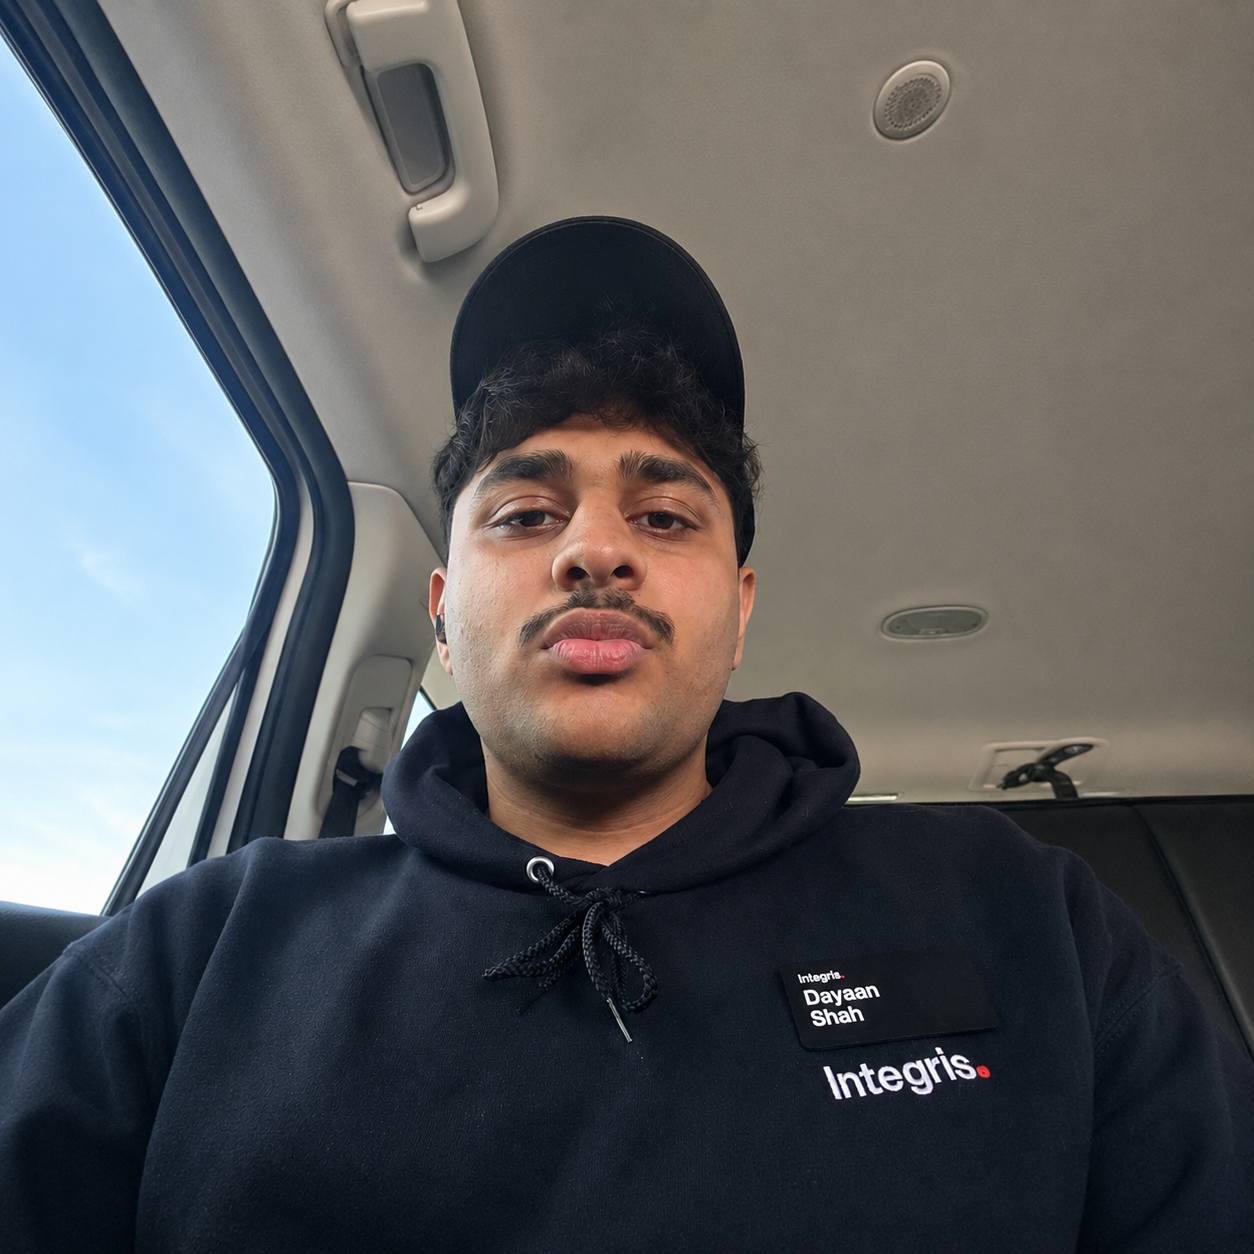
Syed Dayaan Shah
Houston · Sector 01
IT Engineer — Security Operations Focus
Realtime SIEM feed
logs flowingOps telemetry
72% capacityAlerts triaged (24h)
412
MTTD (rolling)
3m 7s
Hosts monitored
214
Risky sign-ins (7d)
9
Active detections
62
Uptime SLO
99.97%
- Initial Access
- Execution
- Persistence
- Priv Esc
- Defense Evasion
- Cred Access
- Discovery
- Lateral
- C2
- Impact
About the operator
ID · OP-SDS-04
- ·Goes by Eddie
- ·21 · Karachi → Dubai → Houston at 12
- ·Lone Star College · AAS Cybersecurity
- ·Xbox loyalist · Watch Dogs 2 & Cricket 26
Hey, I'm Dayaan Shah. I'm 21, and most people who actually know me call me Eddie. I was born in Pakistan, spent my early years bouncing between Karachi and Dubai, and my family moved to Houston when I was 12. Middle school, high school, and college all happened here in Texas. I picked up my Associate in Cybersecurity at Lone Star College, and honestly most of my coursework was networking — VLANs, routing and switching, wireless, firewalls — which is where I really got hooked on this stuff.
Outside of work I'm a pretty heavy gamer. Right now I'm deep into Watch Dogs 2, which is kind of on-brand because that whole hacker vibe is what pulled me into security in the first place. I'm also a big cricket guy, so when I'm not gaming red-team scenarios I'm playing Cricket 26 on my Xbox. And yeah, I'm an Xbox loyalist. PC and PlayStation just aren't for me. During the day I'm an IT Engineer with a security operations focus at Integris, the biggest MSP in the country, after getting promoted out of the support engineer seat, and I'm working my way toward a full SOC analyst role.
Deployment history
Roles across MSP, wireless network administration, and security-analyst work.
- Current Deployment
Jan 2026 — Present
Remote
IT Engineer — Security Operations Focus
Integris
↑ Promoted from IT Support Engineer
- Triage roughly 25–40 SIEM, endpoint, and identity alerts per shift across Microsoft Sentinel and Defender XDR, closing about 85% at my level with a documented determination.
- Investigate Entra ID account-takeover attempts — risky sign-ins, MFA fatigue, token replay — and contain confirmed compromise the same shift, cutting alert-to-containment from hours to under 45 minutes.
- Analyze 50–70 phishing and BEC reports a month with Defender for Office 365, Mimecast, message trace, VirusTotal, and urlscan.io; purge campaigns tenant-wide and tune transport rules.
- Maintain EDR coverage across ~1,500 endpoints (Defender for Endpoint, SentinelOne) and run PowerShell + Microsoft Graph sweeps for bulk sign-in and mailbox-rule audits.
- Map findings to MITRE ATT&CK and document incidents against NIST 800-61 so scope, root cause, and containment are defensible in client review.
- Chapter · 05
Aug 2025 — Jan 2026
Remote
IT Support Engineer
Integris
- Delivered security-focused Tier 1–2 support across SMB and enterprise Microsoft 365 hybrid tenants — identity, endpoint, access control, and network incidents.
- Administered Microsoft 365 and Entra ID: MFA enforcement, Conditional Access, provisioning, mailbox security, and authentication troubleshooting.
- Escalated suspicious sign-ins and account-compromise events to the security team with clean evidence timelines, which led to the move into the security operations seat.
- Chapter · 04
Jan 2025 — Aug 2025
Houston, TX
SOC Analyst I — Security Operations
NetRobin
↑ Promoted from Wireless Network Administrator
- Worked a live queue of 25–40 endpoint and email alerts per shift, escalating confirmed incidents with full timeline, IOCs, and containment recommendation.
- Analyzed 30–40 phishing messages a month using VirusTotal, urlscan.io, and AbuseIPDB; blocked sender infrastructure and pulled matching mail across tenants.
- Hunted beaconing and DNS anomalies in Wireshark and firewall logs; added detections for repeat offenders.
- Ran Nessus and OpenVAS cycles with CVSS-based prioritization, driving critical and high findings down across client sites and verifying with re-scans.
- Chapter · 03
Aug 2024 — Jan 2025
Houston, TX
Wireless Network Administrator
NetRobin
↑ Promoted from Junior IT Support Specialist
- Conducted wireless site surveys; optimized AP placement, VLAN/SSID design, and interference minimization.
- Deployed and hardened WAPs across client campuses, tightening 802.1X/WPA2-Enterprise auth and hunting rogue APs.
- Implemented proactive monitoring and configuration audits to keep networks compliant and performant.
- Chapter · 02
Jan 2024 — Aug 2024
Houston, TX
Junior IT Support Specialist
NetRobin
- Provided Tier 1–2 support for 15+ SMB clients, resolving 20–30 tickets a day via RMM tooling.
- Managed Active Directory, DNS, DHCP, and Microsoft 365 (user creation, MFA setup) to maintain 99% uptime.
- Collaborated with network engineers on secure infrastructure across multi-tenant environments.
- Chapter · 01
Mar 2023 — Jan 2024
Houston, TX
IT Security Analyst Intern
Ai IT Studio
- Supported 10–15 security investigations a week across firewall, endpoint, and email telemetry.
- Assisted with firewall administration, detection tuning, and real-time threat monitoring.
- Ran vulnerability assessments with CVE triage and tracked patch remediation to completion on Windows and Linux endpoints.
Six operations. Four full guided labs.
Every card opens a full write-up. LAB cards ship with an interactive, step-by-step simulation — brief, your move, live result, how I stopped it, how you prevent it.
- Critical▶ Live LabIR-042
Incident Response
Ransomware response — a branching 60-minute drill
Take a live ransomware page from first EDR ping to closed incident. Every decision you make changes what happens next.
EDRIdentity revocationJA3 blocklistsImmutable restore01 / 7Open case → - Critical▶ Live LabPHISH-001
Email / Web Security
Phishing kit dissection — anatomy of a credential harvester
Reverse a captured Microsoft 365 phishing kit, identify the exfil paths, and teach defenders what to look for.
Phishing analysisAiTMKQLMFA-resistant auth02 / 7Open case → - High▶ Live LabIAM-009
Identity / Cryptography
Password brute-force & hash cracking — why length beats complexity
Demonstrate how attackers actually crack passwords and quantify what makes them fail.
bcryptSHA-256Argon2idMFA03 / 7Open case → - High▶ Live LabSOC-014
Detection & Response
SIEM alert triage — separating signal from noise under pressure
Cut analyst time-on-alert by tuning noisy detections and building a repeatable triage loop.
SIEMDetection engineeringSPLATT&CK04 / 7Open case → - Critical▶ Live LabNET-022
Network Forensics
Packet inspection — hunting a C2 beacon inside noisy egress
Find a low-and-slow command-and-control beacon hidden in normal-looking outbound HTTPS.
NetflowTLS metadataEgress filteringIOC hunting05 / 7Open case → - High◇ DemoIAM-014
Identity Security
Entra ID Conditional Access hardening
Reduce identity attack surface for a 300-seat client while keeping legitimate users productive.
Conditional AccessKQLZero TrustIdentity Protection06 / 7Open case → - High◇ DemoVULN-007
Vulnerability Management
60-day CVE remediation program with Nessus
Bring a mid-size client environment from a 127-critical backlog down to zero criticals in 60 days.
NessusPowerShellPatchingReporting07 / 7Open case →
Toolbox & capability matrix
Signal readings — self-assessed proficiency against real production workloads.
SOC / Detection
- SIEM monitoring (Splunk, Sentinel)88%
- Threat detection & hunting84%
- Incident response support86%
- Endpoint security (Defender XDR)85%
Identity & Cloud
- Entra ID / Azure AD90%
- MFA & Conditional Access88%
- Active Directory87%
- Microsoft 365 Security89%
Networking
- LAN/WAN, VLAN, routing & switching92%
- Firewalls & VPN troubleshooting86%
- Wireless (CWNA level)93%
- Wireshark / SNMP / NetFlow84%
Vuln & Scripting
- Nessus / OpenVAS83%
- Python scripting81%
- PowerShell / Bash85%
- IPv4/IPv6 subnetting90%
Certifications & education
- Active
CompTIA Security+
CompTIA · Earned Jun 2026
SOC-track certification — threats, architecture, operations, IR.
- Active
CWNA — Certified Wireless Network Administrator
CWNP · Jan 2023 — Jan 2026
Vendor-neutral 802.11 wireless expertise.
- Active
CCNA: Switching, Routing & Wireless
Cisco · Feb 2025
Enterprise LAN switching, inter-VLAN routing, and wireless fundamentals.
- Active
CCNA: Wireless Networks
Cisco · May 2025
Wireless LAN design, RF fundamentals, and secure Wi-Fi deployment.
- Active
TryHackMe SOC Level 1
TryHackMe · Earned Jul 2026
Hands-on SOC path — SIEM, phishing analysis, threat intel, DFIR.
- Active
IC3 Digital Literacy
Certiport · May 2022
2024 — 2026
Associate's Degree — Cybersecurity
Lone Star College System · Houston, TX
- Coursework: network security, cybersecurity law, database security, OS hardening.
- Lab tools: Kali Linux, Cisco Packet Tracer, Wireshark, cloud security platforms.
Aug 2020 — Jun 2024
High School Diploma — Cybersecurity Career Pathway
Klein Oak High School · Houston, TX
- Hands-on training in network security, digital forensics, ethical hacking.
- Built secure network environments using Packet Tracer and VirtualBox.
Establish a secure channel
Recruiters, hiring managers, and security teams — the fastest path is direct email. Response window: within 24 hours.